WordPress
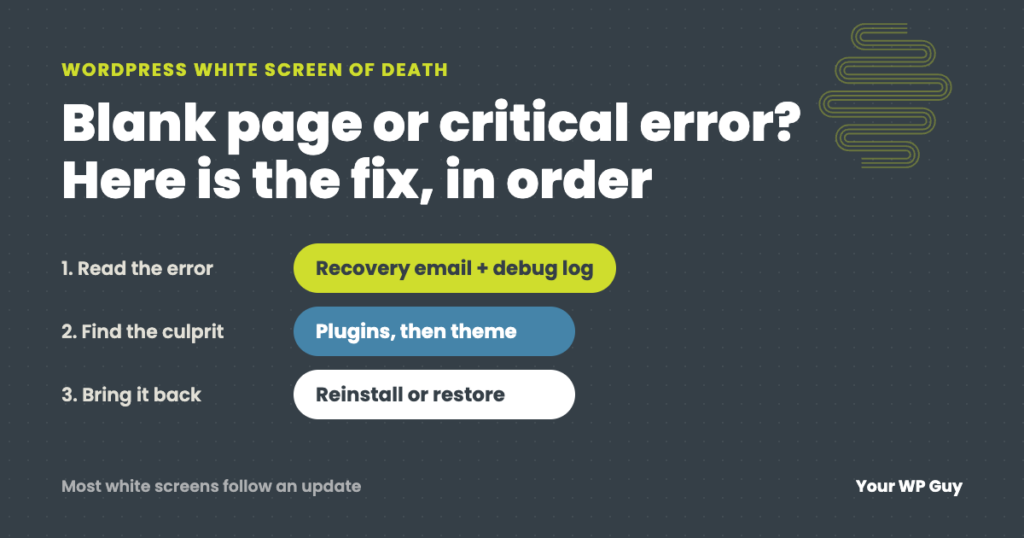
WordPress White Screen of Death (or Critical Error): How to Fix It
Few experiences strike fear into the hearts of website owners quite like seeing the dreaded white screen of death. You log in to check on your site, excited to see your latest blog post. But instead of your beautifully crafted content, you’re met with a blank white screen. No errors, no warnings, just… nothing. This…
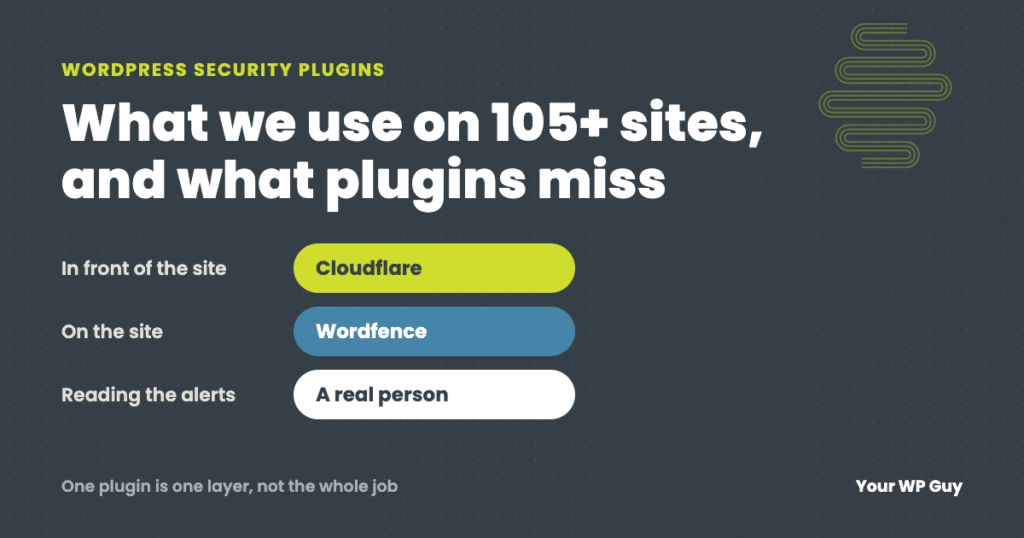
Best WordPress Security Plugins: What We Use on 105+ Sites
The short answer For most WordPress sites, the best security plugin is Wordfence, with Cloudflare in front of the site. Wordfence gives you a firewall, malware scanning and login protection in one plugin. Cloudflare stops bad traffic before it reaches your server. Run one all-in-one security plugin, not two. A plugin is only one layer,…
Card Testing Attack Case Study: Stopped Before a Dollar Was Lost
Over 100 stolen card numbers hit a client checkout in a single week. Here is how we spotted the card testing attack, what it could have cost, and the fix that shut it down.
WordPress Site Speed Audit: The 8MB That Most Tools Missed
A WordPress site speed audit uncovered 8.2MB of media hidden behind a CDN blind spot, invisible to GTmetrix and PageSpeed. Here is what we found and how we fixed it.
Case Study: The Missing Line of Code That Cost a Nonprofit 40 Seconds
A nonprofit client’s WordPress site looked fine on office WiFi, but took over 40 seconds to load on mobile. The cause was a single missing line of code silently disabling image lazy loading site wide. Here is the detective work behind the fix, and how total mobile load time dropped 72 percent in a day.
Why Cloudflare Alone Won’t Protect Your WooCommerce Store
Cloudflare only protects traffic that actually goes through it. Here are the two ways attackers get around it, and the three layers that close the gap for good.
Anatomy of a WordPress Breach: A One-Day-Old Plugin Flaw, an Invisible Admin, and How We Shut It Down
A real WordPress security breach from our managed care fleet. An attacker used a newly disclosed plugin vulnerability to bypass the login screen entirely, planted two hidden backdoors, and created an admin account that respawned on every page load. Here is what we found and the exact order of operations that shut it down.
What Caused the WordPress Hosting Outage on August 13, 2026 (And What We Are Doing About It)
A storm-driven cooling failure at a Phoenix data center knocked some WordPress sites offline on August 13, 2026. Here is what happened, why it was not a security issue, and the failover system we are rolling out so it does not take every site down at once next time.
5 WordPress Security Rules Your Site Is Probably Missing
The Short Version These 5 WordPress security rules close off most of what automated attacks are looking for. Most sites are missing at least one. Most attacks aren’t sophisticated. They’re bots running down a checklist of common weaknesses, hoping yours is unlocked. Never let PHP run in your uploads folder, that’s how a single bad…
Site Slow Under Load? A Real Case Study in Why
A client’s site slowed to a crawl under load, but the server had power to spare. Here is the real cause we found and the fix that made it 30x faster at no added cost.