Abandoned WordPress Plugins: How to Spot Them and What to Do
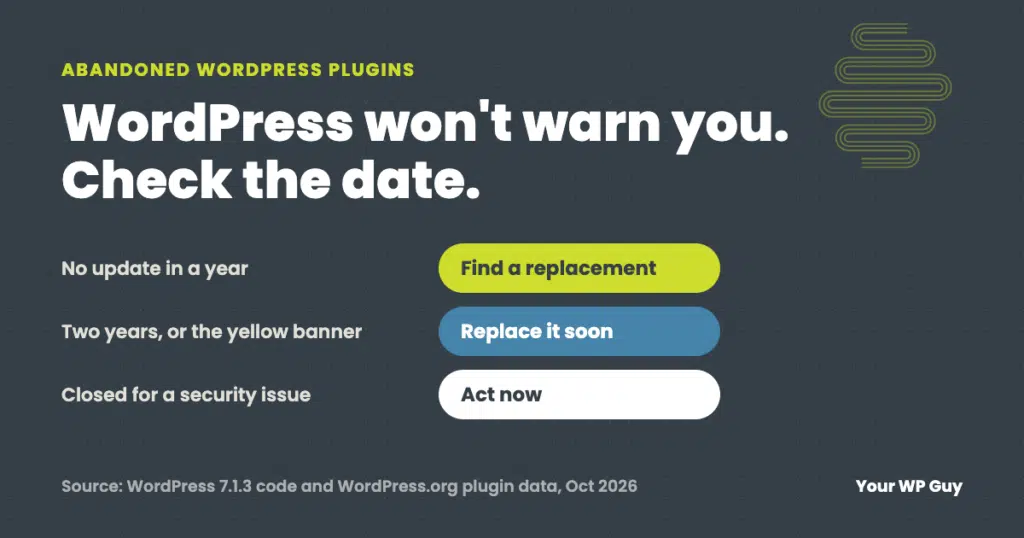
An abandoned WordPress plugin is one its developer no longer updates. It may keep working for years, but any security hole found in it will never be fixed, and it can break the next time WordPress or PHP changes. WordPress does not warn you, so check each plugin’s “Last updated” date. No update in a year: start looking for a replacement. Two years: replace it soon. Closed for a security issue: act now.
Plugins are what make WordPress useful, and most sites run a dozen or more. Each one is written and kept up by its own developer, and developers move on. When they do, the plugin keeps running on your site as if nothing happened.
We keep WordPress sites updated for small businesses every day, so this guide covers what we actually check: the difference between an outdated, an abandoned and a closed plugin, what the warnings really mean, and how to decide whether to keep, replace or rebuild one.
Outdated, abandoned or closed?
These three get mixed up, but each has a different sign and a different deadline:
| The plugin is | What you see | What it means | What to do |
|---|---|---|---|
| Outdated | An update is waiting on your Plugins screen | The developer fixed something and you have not installed it | Back up and update it |
| Abandoned | No update waiting, and none for a year or more | No update is coming, even for security holes | Plan a replacement |
| Closed | “This plugin has been closed” on its WordPress.org page | WordPress.org pulled it from the directory | Find out why. A security closure means act now |
“This plugin hasn’t been tested with the latest 3 major releases of WordPress”
This yellow banner on a WordPress.org plugin page reads in full: “This plugin hasn’t been tested with the latest 3 major releases of WordPress. It may no longer be maintained or supported and may have compatibility issues when used with more recent versions of WordPress.”
It is based on the plugin’s “Tested up to” version, not on when it was last updated. With WordPress 7.1 current, any plugin tested only up to a version below 6.9 gets the banner. So a plugin updated last month can still show it, and a plugin untouched for two years may not. Treat it as a reason to look closer, not as proof.
“This plugin has been closed”
A closed plugin’s page says “This plugin has been closed as of” a date, “and is not available for download”, and whether the closure is permanent or temporary. Nobody can download or install it any more. WordPress.org lists six reasons: Security Issue, Author Request, Guideline Violation, Licensing/Trademark Violation, Merged into Core and Unused.
For most closures, the reason stays hidden for the first 60 days. A plugin closed last week tells you when, but not why. Until you know, treat it as a security closure. Security closures can be reopened once the developer fixes the problem.
Why WordPress does not warn you
WordPress shows nothing on your Plugins screen when a plugin is abandoned or closed. We checked the code of WordPress 7.1.3: there is no message for either. A closed plugin simply never gets another update, and the screen looks normal. Patchstack, a WordPress security company, says the same in its 2025 report: abandoned plugins are not flagged for users, even when they are removed for security reasons.
WordPress only shows compatibility in a few places: on the cards when you add a new plugin (“Untested with your version of WordPress”), in a plugin’s “View details” window, and on the Updates screen for plugins that have an update waiting. A security plugin can do more. Wordfence, for example, flags a WordPress.org plugin as abandoned when its last update is about two years old, and raises a critical alert when a plugin “has been removed from wordpress.org but is still installed on your site.”
The scale is real. By our count of the WordPress.org plugin data in October 2026, about 46% of the 77,000+ plugins in the directory have not been updated in two years. Patchstack reported 827 abandoned plugins and themes to WordPress.org in 2023, and in 2024, 1,614 plugins and themes were removed from the directory for unpatched security issues. Our guide to WordPress security issues covers what attackers do with those holes.
How to check your plugins in two minutes
- List your plugins. Go to Plugins in your dashboard. For each one, click “View details” and note “Last updated” and “Tested up to”.
- Look it up on WordPress.org. Open the plugin’s page and look for the yellow “hasn’t been tested” banner or the red “closed” notice. Check the Support tab too: questions with no answer from the developer for months are a bad sign, and so are other plugins by the same developer that have all gone quiet.
- Check a closed plugin’s reason. This address shows WordPress.org’s record for any plugin, including the closure date and reason. Replace PLUGIN-SLUG with the plugin’s folder name:
https://api.wordpress.org/plugins/info/1.2/?action=plugin_information&request[slug]=PLUGIN-SLUG - Or list everything at once. If your host gives you WP-CLI, this shows every plugin, whether it is active, its version and whether an update is waiting:
wp plugin list --fields=name,status,version,update
Then sort what you found:
- No update in a year: start looking for a replacement. The plugin may be fine, but you want a plan before you need one.
- Two years, or the “hasn’t been tested” banner: replace it soon. This is where security tools start flagging it.
- Last updated before PHP 8.0 (November 2020), or closed for a security issue: act now. Old code like that was never built for current PHP and is the most likely thing to break when your server moves to a newer version.
Our rule of thumb: plugins should be swappable, like a brick in a Lego set. A plugin you can replace in an afternoon is a small risk. A plugin your whole site is built on is the one to watch closely.
When “no updates” is not abandonment
Some plugins look abandoned but are not:
- Premium plugins have no WordPress.org page and only update while your license is active. An expired license looks exactly like a dead plugin.
- Plugins bundled with a theme only update when the theme does. Our guide to WordPress themes has a case where that went wrong.
- A closed listing with the same name. A plugin’s old free listing on WordPress.org can be closed while the real product is sold and updated elsewhere. Check where your copy actually comes from before you panic.
The opposite is also true: a plugin that is updated can still be a risk. In April 2026, a security researcher reported that a buyer of a group of plugins had hidden a backdoor in a routine-looking update. WordPress.org closed them, including Countdown Timer Ultimate (closed April 7, 2026, Reason: Security Issue). Popular and updated is not the same as safe, so it is worth noticing when a plugin changes hands.
A real example: the add-on that looked abandoned
A landscaping company’s site broke on its last round of updates, so it was rolled back and then left frozen on early-2023 software. When we looked, the cause was one third-party add-on pack that had silently stopped receiving updates, and it supplied 313 of the site’s 636 building blocks.
It looked abandoned, but it was a license problem, not a missing developer. We licensed the add-on and brought the whole site current in one afternoon. All 22 pages rendered the same on phone and desktop afterward. Removing it would have meant rebuilding half the site.
Keep, replace, remove or rebuild
- Find out what it does on your site first. Look for its shortcodes in your pages, forms it runs, data it stores and other plugins that depend on it. That tells you what will break without it.
- Back up before you change anything. Deleting a plugin can run its clean-up routine and remove its settings and data for good.
- Replace it with a maintained plugin that does the same job, tested on a copy of the site where possible.
- Remove it if you no longer need it. Delete it, don’t just deactivate it: a deactivated plugin’s files are still on the server and can still be attacked.
- Keep it only for a while, with protection, if there is no replacement yet: a firewall, vulnerability monitoring, as few admin users as possible, and a tested backup.
- Have it rebuilt when nothing else does the job. A custom plugin built for your site, that you own, replaces the dependency for good.
If a plugin already broke something, our one-time WordPress fix gets the site working again first.
Rather have someone check your plugins?
We check every plugin on your site, tell you which ones to worry about, and replace the risky ones.
- Talk to us about your siteA quick call about what your site does and what it runs.
- We check every pluginUpdates, closures, licenses and what each one does on your site.
- You get a plain-English planWhat to keep, what to replace, and what we can take off your hands.
Wondering what else is out of date? Our free Uh Oh Score checks your site and shows what to fix first, with no sales call required.
Get my Uh Oh ScoreQuestions people ask
How do I know if a WordPress plugin is abandoned?
Check its “Last updated” date and “Tested up to” version under View details, then look at its WordPress.org page for a “hasn’t been tested” or “closed” notice and at its support forum for unanswered questions. No update in a year means start looking for a replacement; two years means replace it soon.
What does “This plugin has been closed” mean?
WordPress.org removed the plugin from its directory, so nobody can download or install it. The reason can be a security issue, the author’s request, a guideline violation, a licensing or trademark problem, being merged into WordPress, or not being used. For most closures, the reason stays hidden for 60 days, so treat a new closure as a security closure until you know.
Is it safe to keep using an abandoned plugin?
It depends on what it does and whether a security hole is known in it. A small plugin with no known problems is a low risk for a while; a plugin with a known hole, or one that handles logins, forms or payments, should be replaced now. Either way, plan the replacement.
Why didn’t WordPress warn me?
WordPress shows no warning for abandoned or closed plugins. It only shows compatibility notes when you add a plugin, in its View details window and for plugins with an update waiting. A security plugin such as Wordfence can flag abandoned and removed plugins for you.
Is a deactivated plugin still a risk?
Yes. Its files stay on your server and can still be attacked. If you do not need it, back up the site and delete it, after checking whether it stores data you want to keep.
Can plugins contain malware?
Yes. In 2026, WordPress.org closed a group of plugins after a security researcher reported that their new owner had hidden a backdoor in an update. If you think a plugin has already infected your site, get the site cleaned, not just the plugin removed.
Can someone take over an abandoned plugin?
Sometimes. WordPress.org lets developers adopt plugins, but the original developer is contacted first, the code has to be fixed, and closed plugins are less likely to be adopted. For your own site, it is usually faster to replace the plugin or have a custom one built.
Sources
- WordPress.org, Plugin Developer FAQ (closed plugins) and Taking over an existing plugin (checked October 2026).
- WordPress.org plugin directory data (our count of last-updated dates, October 2026) and the Countdown Timer Ultimate closure notice.
- Patchstack, State of WordPress Security in 2024 and in 2025.
- PHP Manual, create_function (removed in PHP 8.0).
Keep your website working as hard as you do
We update, back up, monitor and protect your WordPress site every day, and flag plugins that stop getting updates before they become a problem.
Jonathan Wofford is the founder of Your WP Guy, a WordPress care and maintenance service supporting 105+ active client sites. He and his team keep WordPress sites fast, secure, and running, so business owners can stay focused on their business instead of their website.