
wordpress plugins
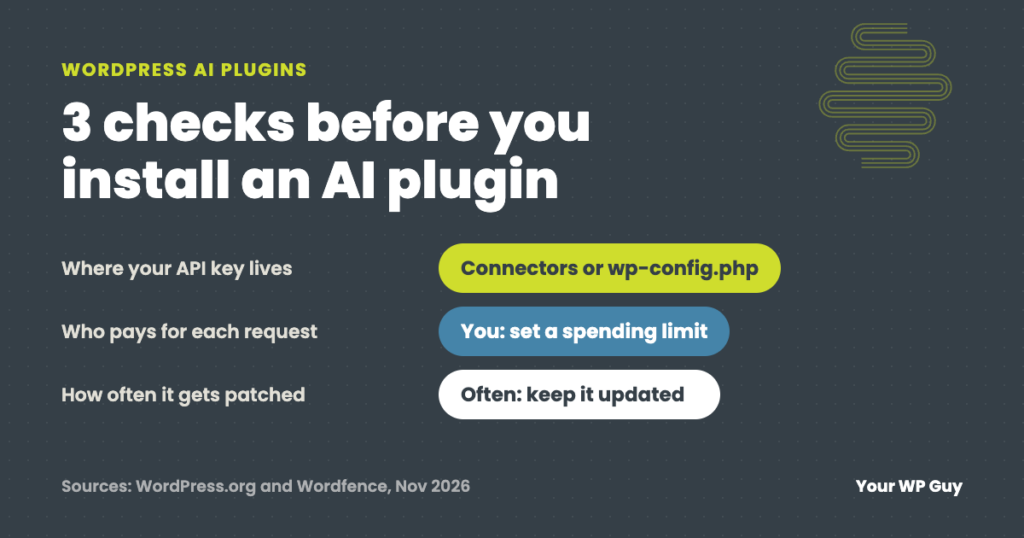
WordPress AI Plugins: What to Check Before You Install One
The short answer A WordPress AI plugin connects your site to an AI service so it can write, answer chats, tag images or take actions for you. Before you install one, check where it keeps your API key, what the usage bill will be, what data it sends out, how often it gets security fixes…
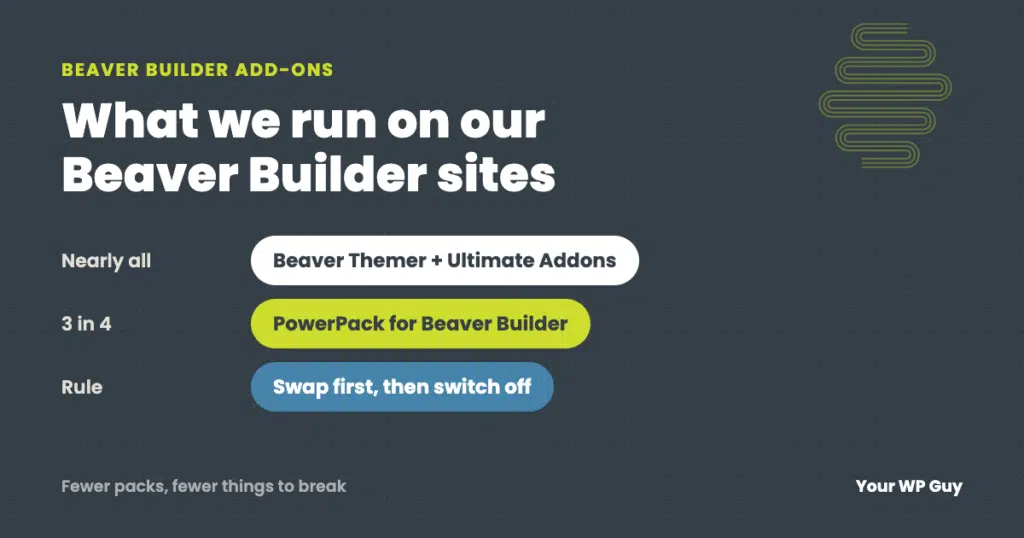
Best Beaver Builder Add-ons: What We Actually Use
The short answer Most Beaver Builder sites need only two or three add-ons. On the sites we look after, the core stack is Beaver Themer (now included in every Beaver Builder plan), Ultimate Addons for Beaver Builder and PowerPack. Add one pack at a time, switch off the modules you don’t use, and only stack…
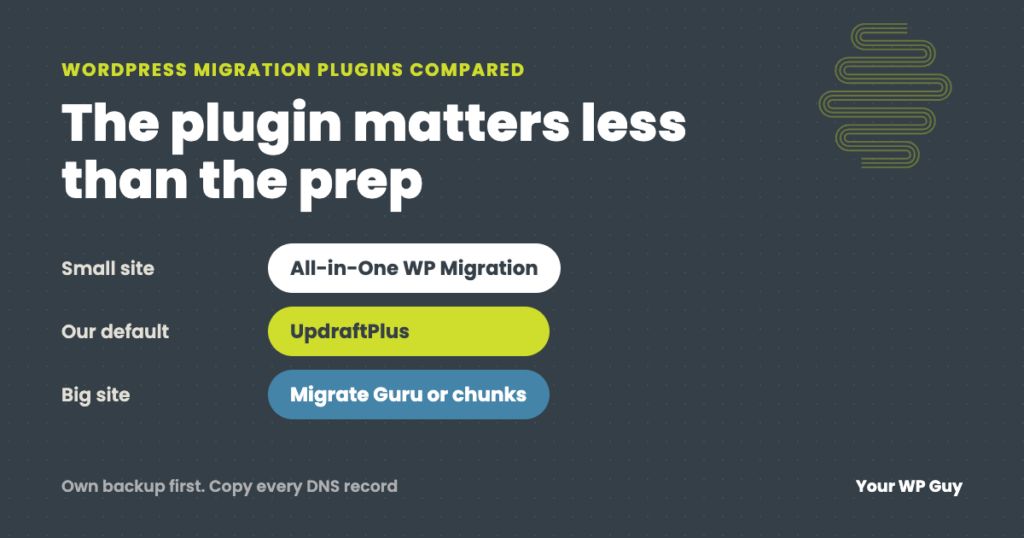
Best WordPress Migration Plugins: What We Use and When Each Fits
The short answer For most sites, use a backup plugin you already trust, and test the move before you switch. We have used all six plugins below on client moves, and UpdraftPlus is our default because it works most consistently. All-in-One WP Migration is simplest for small sites, Duplicator suits moves to an empty server,…
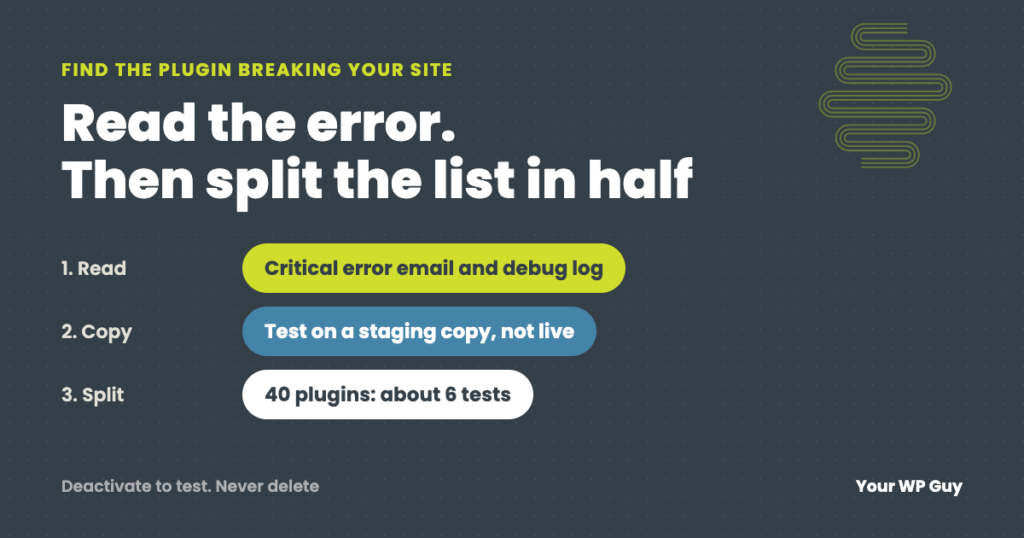
How to Find Which Plugin Is Breaking Your WordPress Site
The short answer Read the error before you start switching plugins off. WordPress’s “critical error” email and your debug log often name the plugin that failed. If there is no error, copy the site to a staging site, turn off half the plugins, and check if the problem goes away. Keep halving the suspect group…
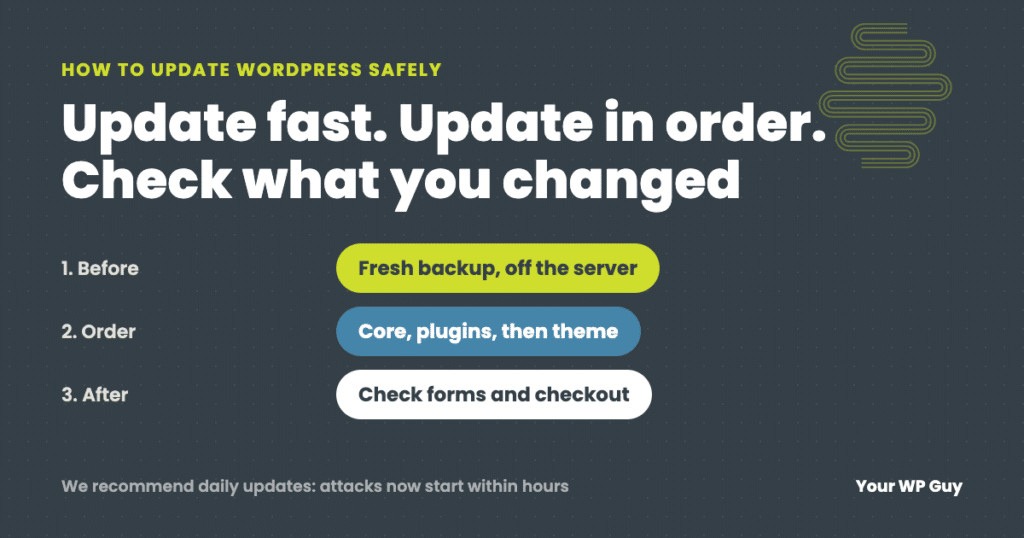
How to Update WordPress Safely (Without Breaking Your Site)
The short answer To update WordPress safely, make a fresh backup, then update in this order: PHP (if needed), WordPress core, plugins a few at a time, then your theme, and check the site after each step, including forms and checkout. We recommend updating daily, because with AI, attacks on a newly published flaw now…
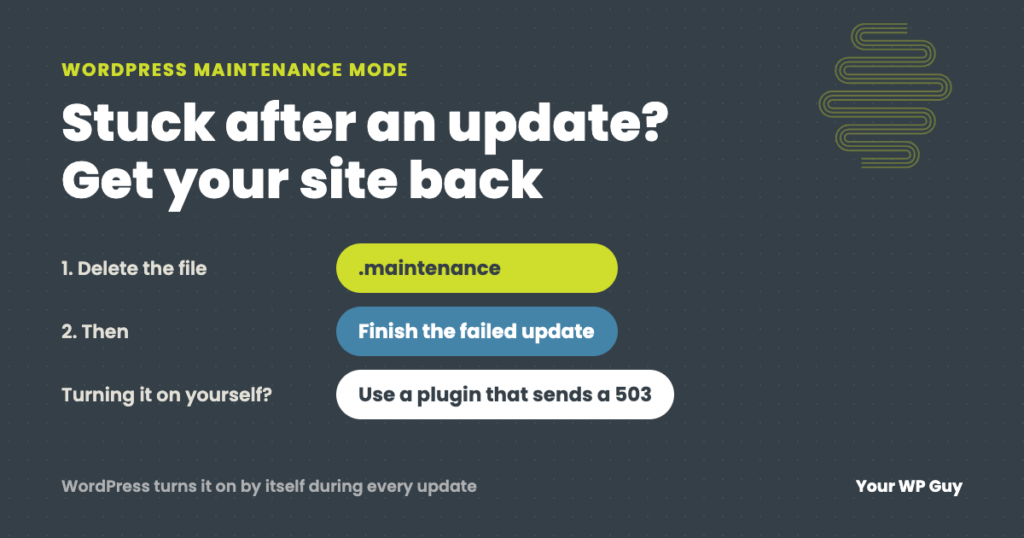
WordPress Maintenance Mode: Fix a Stuck Site or Turn It On Safely
The short answer WordPress puts your site in maintenance mode by itself for a few seconds every time it updates. If an update hangs, the site gets stuck showing “Briefly unavailable for scheduled maintenance. Check back in a minute.” To fix it, delete the .maintenance file in your site’s main folder, then finish the update…
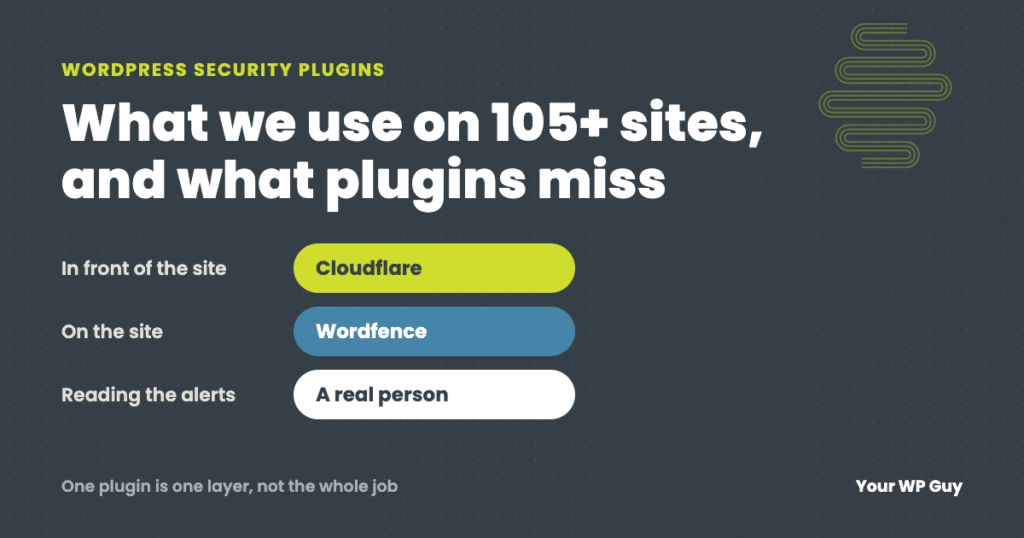
Best WordPress Security Plugins: What We Use on 105+ Sites
The short answer For most WordPress sites, the best security plugin is Wordfence, with Cloudflare in front of the site. Wordfence gives you a firewall, malware scanning and login protection in one plugin. Cloudflare stops bad traffic before it reaches your server. Run one all-in-one security plugin, not two. A plugin is only one layer,…

LiteSpeed Cache Vulnerability – Unauthenticated Sensitive Information Exposure via Log Files – CVE-2024-44000 | WordPress Plugin Vulnerability Report
Plugin Name: LiteSpeed Cache Key Information: Software Type: Plugin Software Slug: litespeed-cache Software Status: Active Software Author: litespeedtech Software Downloads: 79,208,611 Active Installs: 6,000,000 Last Updated: September 6, 2024 Patched Versions: 6.5.0.1 Affected Versions: <= 6.4.1 Vulnerability Details: Name: LiteSpeed Cache <= 6.4.1 Type: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N CVE: CVE-2024-44000 CVSS Score: 7.5 Publicly Published: September 5, 2024…
LiteSpeed Cache Vulnerability – Unauthenticated Privilege Escalation – CVE-2024-28000 | WordPress Plugin Vulnerability Report
Plugin Name: LiteSpeed Cache Key Information: Software Type: Plugin Software Slug: litespeed-cache Software Status: Active Software Author: litespeedtech Software Downloads: 75,818,864 Active Installs: 5,000,000 Last Updated: August 21, 2024 Patched Versions: 6.4 Affected Versions: <= 6.3.0.1 Vulnerability Details: Name: LiteSpeed Cache <= 6.3.0.1 Title: Unauthenticated Privilege Escalation Type: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H CVE: CVE-2024-28000 CVSS Score: 9.8 Publicly…
String Locator Vulnerability – Reflected Cross-Site Scripting – CVE-2023-6987 | WordPress Plugin Vulnerability Report
Plugin Name: String Locator Key Information: Software Type: Plugin Software Slug: string-locator Software Status: Active Software Author: instawp Software Downloads: 1,093,003 Active Installs: 100,000 Last Updated: August 23, 2024 Patched Versions: 2.6.6 Affected Versions: <= 2.6.5 Vulnerability Details: Name: String Locator <= 2.6.5 Title: Reflected Cross-Site Scripting Type: CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N CVE: CVE-2023-6987 CVSS Score: 6.1 Publicly…