
security
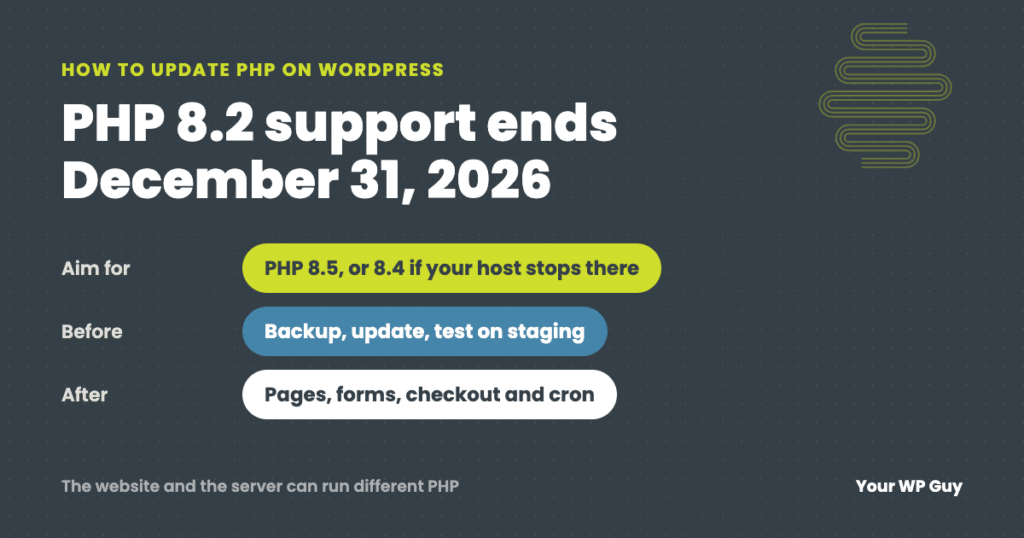
How to Update PHP on WordPress (Without Breaking Your Site)
The short answer Move to PHP 8.5 if your host offers it, or 8.4 if it does not. PHP 8.2 stops getting security fixes on December 31, 2026. Back up, update everything and test on a staging copy first. Then change the version in your hosting control panel and check your pages, forms, checkout and…

Happy Addons for Elementor Vulnerability – Reflected Cross-Site Scripting – CVE-2023-6632 | WordPress Plugin Vulnerability Report
Plugin Name: Happy Addons for Elementor Key Information: Software Type: Plugin Software Slug: happy-elementor-addons Software Status: Active Software Author: thehappymonster Software Downloads: 5,728,647 Active Installs: 400,000 Last Updated: January 5, 2024 Patched Versions: 3.10.0 Affected Versions: <= 3.9.1.1 Vulnerability Details: Name: Happy Addons for Elementor <= 3.9.1.1 – Reflected Cross-Site Scripting Title: Reflected Cross-Site Scripting Type: Improper Neutralization of Input During Web Page Generation (‘Cross-site Scripting’) CVE: CVE-2023-6632…
WordPress Plugin Vulnerability Report – Backup Migration – Unauthenticated Remote Code Execution – CVE-2023-6553
Plugin Name: Backup Migration Key Information: Software Type: Plugin Software Slug: backup-backup Software Status: Active Software Author: migrate Software Downloads: 1,095,099 Active Installs: 90,000 Last Updated: December 11, 2023 Patched Versions: 1.3.8 Affected Versions: <= 1.3.7 Vulnerability Details: Name: Backup Migration <= 1.3.7 – Unauthenticated Remote Code Execution Type: Improper Control of Generation of Code (‘Code Injection’) CVE: CVE-2023-6553 CVSS Score: 9.8 (Critical) Publicly Published: December 11, 2023 Researcher: Nex…

WordPress Plugin Vulnerability Report – SpeedyCache – Missing Authorization via speedycache_create_test_cache
Plugin Name: SpeedyCache Key Information: Software Type: Plugin Software Slug: speedycache Software Status: Active Software Author: softaculous Software Downloads: 746,740 Active Installs: 100,000 Last Updated: December 1, 2023 Patched Versions: 1.1.3 Affected Versions: <= 1.1.2 Vulnerability Details: Name: SpeedyCache <= 1.1.2 – Missing Authorization via speedycache_create_test_cache Title: Missing Authorization via speedycache_create_test_cache Type: Missing Authorization CVSS Score: 4.3 (Medium) Publicly Published: December 1, 2023 Description: The SpeedyCache – Cache, Optimization, Performance…
WordPress Plugin Vulnerability Report – Migration, Backup, Staging – WPvivid – Missing Authorization & Stored Cross-Site Scripting
Plugin Name: Migration, Backup, Staging – WPvivid Key Information: Software Type: Plugin Software Slug: wpvivid-backuprestore Software Status: Active Software Author: wpvividplugins Software Downloads: 5,141,419 Active Installs: 300,000 Last Updated: September 12, 2023 Patched Versions: 0.9.91 Affected Versions: <=0.9.90 First Vulnerability: Vulnerability Details: Name: WPvivid Backup Plugin <= 0.9.90 – Missing Authorization via ‘start_staging’ and ‘get_staging_progress’…
WordPress Plugin Vulnerability Report: Slimstat Analytics – Authenticated (Contributor+) Blind SQL Injection via Shortcode – CVE-2023-4598
Key Information: Software Type: Plugin Software Slug: wp-slimstat Software Status: Active Software Author: mostafas1990 Software Downloads: 5,922,898 Active Installs: 100,000 Last Updated: September 11, 2023 Patched Versions: 5.0.10 Affected Versions: <=5.0.9 Vulnerability Details: Name: Slimstat Analytics <= 5.0.9 – Authenticated (Contributor+) Blind SQL Injection via Shortcode Type: Improper Neutralization of Special Elements used in an…
WordPress Plugin Vulnerability Report: EWWW Image Optimizer – Sensitive Information Exposure
Plugin Name: EWWW Image Optimizer Key Information: Software Type: Plugin Software Slug: ewww-image-optimizer Software Status: Active Software Author: nosilver4u Software Downloads: 33,159,954 Active Installs: 1,000,000 Last Updated: September 7, 2023 Patched Versions: 7.2.1 Affected Versions: <7.2.1 Vulnerability Details: Name: EWWW Image Optimizer <= 7.2.0 – Sensitive Information Exposure Type: Information Exposure CVSS Score: 5.3 (medium)…
WordPress Plugin Vulnerability Report: EmbedPress – Cross-Site Request Forgery
Plugin Name: EmbedPress Key Information: Software Type: Plugin Software Slug: embedpress Software Status: Active Software Author: wpdevteam Software Downloads: 1,709,151 Active Installs: 80,000 Last Updated: September 8, 2023 Patched Versions: 3.8.4 Affected Versions: <3.8.4 Vulnerability Details: Name: EmbedPress <= 3.8.3 – Cross-Site Request Forgery Type: Cross-Site Request Forgery (CSRF) CVSS Score: 4.3 (Medium) Publicly Published:…
WordPress Plugin Vulnerability Report: User Feedback – Unauthenticated Stored Cross-Site Scripting – CVE-2023-39308
Plugin Name: User Feedback Key Information: Software Type: Plugin Software Slug: userfeedback-lite Software Status: Active Software Author: smub Software Downloads: 348,588 Active Installs: 100,000 Last Updated: September 7, 2023 Patched Versions: 1.0.8 Affected Versions: <=1.0.7 Vulnerability Details: Name: User Feedback <= 1.0.7 – Unauthenticated Stored Cross-Site Scripting Type: Improper Neutralization of Input During Web Page…