Plugin Updates
How to Update WordPress Safely (Without Breaking Your Site)
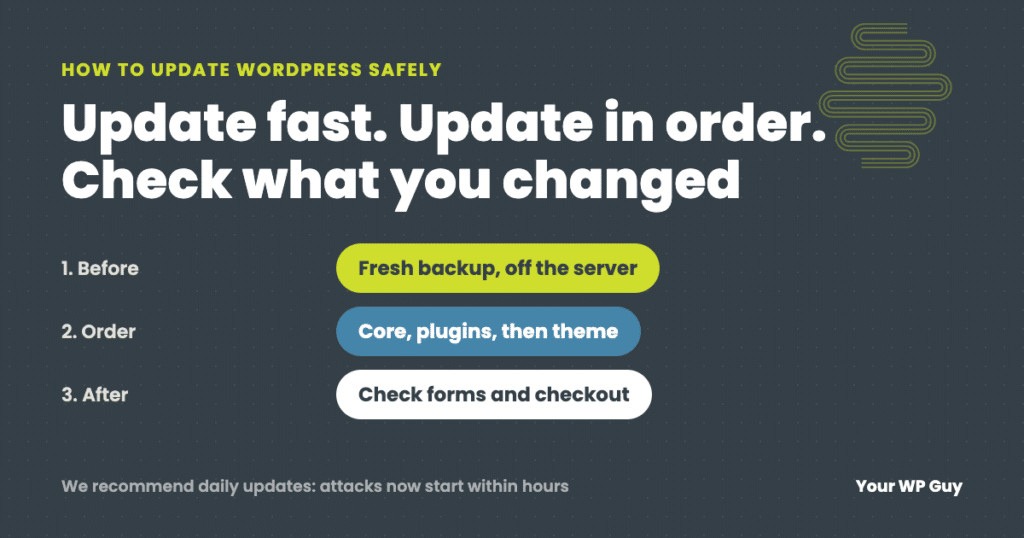
The short answer To update WordPress safely, make a fresh backup, then update in this order: PHP (if needed), WordPress core, plugins a few at a time, then your theme, and check the site after each step, including forms and checkout. We recommend updating daily, because with AI, attacks on a newly published flaw now…
Is WordPress Secure? The Real Security Issues and How Sites Get Hacked
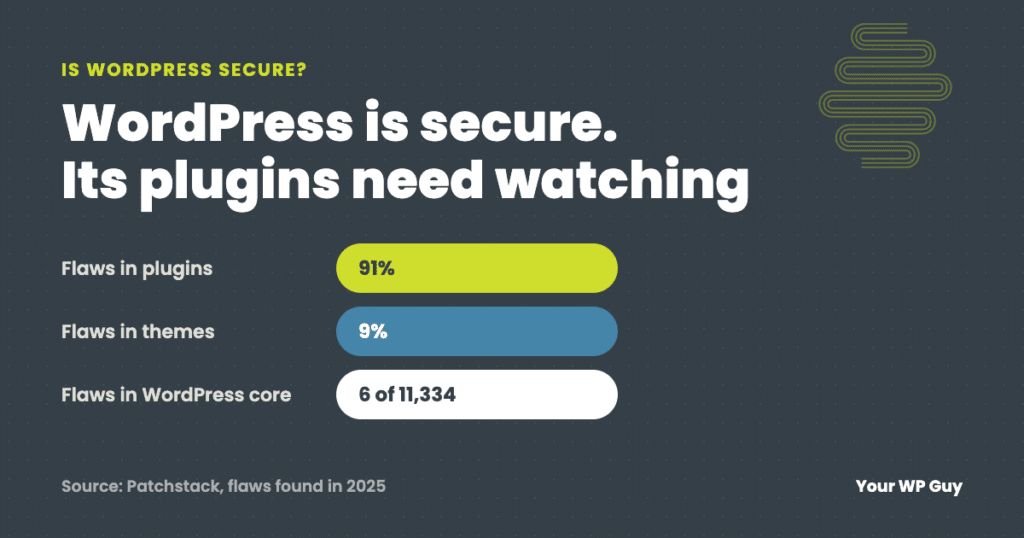
The short answer Yes, WordPress itself is secure: only 6 of the 11,334 WordPress security flaws found in 2025 were in WordPress core, all low priority. The real security issues are plugins (91%) and themes (9%), weak logins, and updates that wait too long, because attacks on a new flaw often start within hours, and…

Mollie Payments for WooCommerce Vulnerability – Unauthenticated Full Path Disclosure – CVE-2024-6448 | WordPress Plugin Vulnerability Report
Plugin Name: Mollie Payments for WooCommerce Key Information: Software Type: Plugin Software Slug: mollie-payments-for-woocommerce Software Status: Active Software Author: mollieintegration Software Downloads: 3,421,407 Active Installs: 100,000 Last Updated: August 27, 2024 Patched Versions: 7.8.0 Affected Versions: <= 7.7.0 Vulnerability Details: Name: Mollie Payments for WooCommerce <= 7.7.0 Type: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N CVE: CVE-2024-6448 CVSS Score: 5.3 Publicly…
User Feedback – Create Interactive Feedback Form, User Surveys, and Polls in Seconds Vulnerability – Unauthenticated Stored Cross-Site Scripting via Name Parameter – CVE-2024-5902 | WordPress Plugin Vulnerability Report
Plugin Name: User Feedback – Create Interactive Feedback Form, User Surveys, and Polls in Seconds Key Information: Software Type: Plugin Software Slug: userfeedback-lite Software Status: Active Software Author: smub Software Downloads: 1,961,766 Active Installs: 200,000 Last Updated: August 8, 2024 Patched Versions: 1.0.16 Affected Versions: <= 1.0.15 Vulnerability Details: Name: UserFeedback Lite <= 1.0.15 Title:…
VK All in One Expansion Unit – Authenticated (Contributor+) Stored Cross-Site Scripting via className – CVE-2024-2170 |WordPress Plugin Vulnerability Report
Plugin Name: VK All in One Expansion Unit Key Information: Software Type: Plugin Software Slug: vk-all-in-one-expansion-unit Software Status: Active Software Author: kurudrive Software Downloads: 5,085,263 Active Installs: 100,000 Last Updated: March 25, 2024 Patched Versions: 9.97.0.0 Affected Versions: <= 9.96.0.1 Vulnerability Details: Name: VK All in One Expansion Unit <= 9.96.0.1 Title: Authenticated (Contributor+) Stored…
User Feedback Vulnerability – Unauthenticated Stored Cross-Site Scripting – CVE-2024-0903 | WordPress Plugin Vulnerability Report
Plugin Name: User Feedback Key Information: Software Type: Plugin Software Slug: userfeedback-lite Software Status: Active Software Author: smub Software Downloads: 1,054,695 Active Installs: 200,000 Last Updated: February 21, 2024 Patched Versions: 1.0.14 Affected Versions: <= 1.0.13 Vulnerability Details: Name: User Feedback – Create Interactive Feedback Form, User Surveys, and Polls in Seconds <= 1.0.13 – Unauthenticated Stored Cross-Site Scripting Title: Unauthenticated Stored Cross-Site Scripting Type: Improper Neutralization…

Elementor Addon Elements Vulnerability – Authenticated (Contributor+) Stored Cross-Site Scripting – CVE-2024-0834 |WordPress Plugin Vulnerability Report
Plugin Name: Elementor Addon Elements Key Information: Software Type: Plugin Software Slug: addon-elements-for-elementor-page-builder Software Status: Active Software Author: webtechstreet Software Downloads: 2,364,972 Active Installs: 100,000 Last Updated: February 8, 2024 Patched Versions: 1.12.12 Affected Versions: 1.12.11 – 1.12.11 Vulnerability Details: Name: Elementor Addon Elements <= 1.12.11 Title: Authenticated (Contributor+) Stored Cross-Site Scripting Type: CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:N CVE:…
Starbox Vulnerability – the Author Box for Humans – Insecure Direct Object Reference – CVE-2024-0366 | WordPress Plugin Vulnerability Report
Plugin Name: Starbox – the Author Box for Humans Key Information: Software Type: Plugin Software Slug: starbox Software Status: Active Software Author: cifi Software Downloads: 441,960 Active Installs: 50,000 Last Updated: February 1, 2024 Patched Versions: 3.4.8 Affected Versions: <= 3.4.7 Vulnerability Details: Name: Starbox – the Author Box for Humans <= 3.4.7 Title: Insecure…
The Events Calendar Vulnerability – Unauthenticated Sensitive Information Exposure – CVE-2023-6557 | WordPress Plugin Vulnerability Report
Plugin Name: The Events Calendar Key Information: Software Type: Plugin Software Slug: the-events-calendar Software Status: Active Software Author: theeventscalendar Software Downloads: 53,054,073 Active Installs: 700,000 Last Updated: January 12, 2024 Patched Versions: 6.2.9 Affected Versions: <= 6.2.8.2 Vulnerability Details: Name: The Events Calendar <= 6.2.8.2 Title: Unauthenticated Sensitive Information Exposure Type: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N CVE: CVE-2023-6557 CVSS…

What are Abandoned WordPress Plugins?
Imagine you own a small online business. You built your website on WordPress and installed a few plugins to add useful features like contact forms, social sharing buttons, and SEO optimization. These plugins worked great initially. But over time some of them have stopped receiving updates. The developers seem to have abandoned these plugins altogether.…