Security
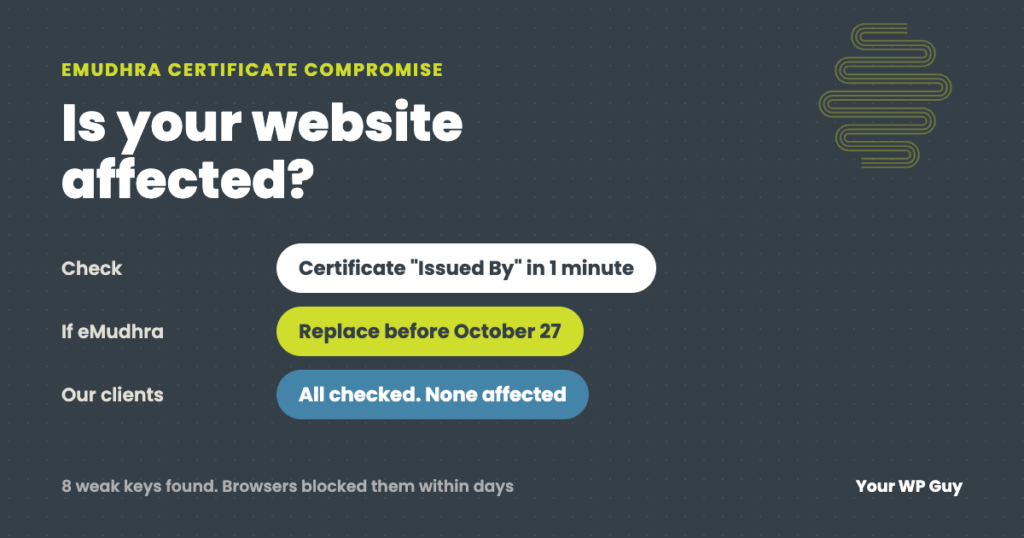
eMudhra Certificate Compromise: Is Your Website Affected?
The short answer In October 2026, eight intermediate certificates from the certificate authority eMudhra were found to have private keys so weak that anyone could recover them. In theory that let someone create a fake certificate for any website. Browsers blocked the certificates within days, and no misuse has been confirmed. Your website is only…
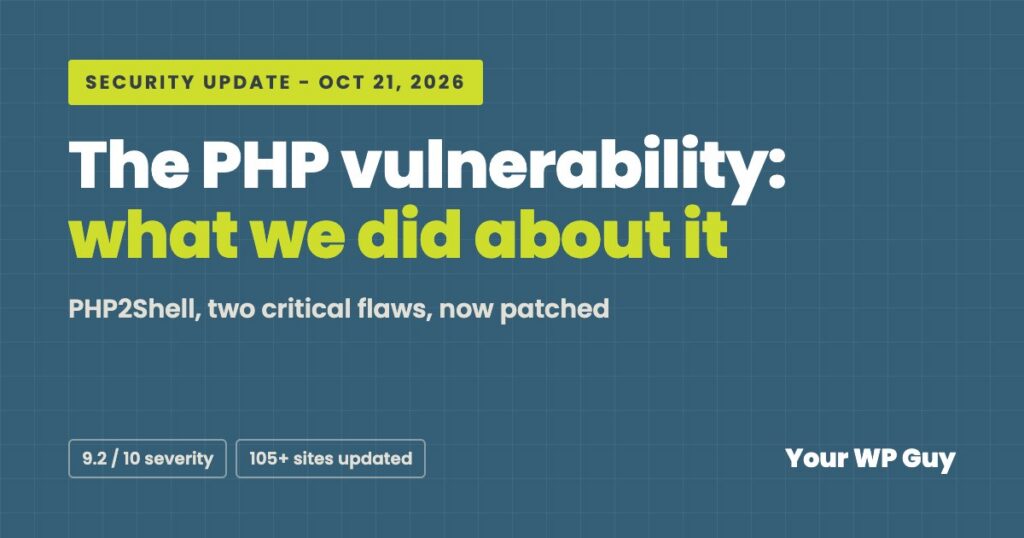
PHP Vulnerability (PHP2Shell): What We Did to Protect Your WordPress Site
TL;DR: On October 21, 2026, PHP, the language WordPress runs on, released emergency fixes for two critical security flaws. Hosting companies around the world have been racing to patch. Your WP Guy checked every site in our care and moved each one to a secure, patched version of PHP. A few older sites may behave…
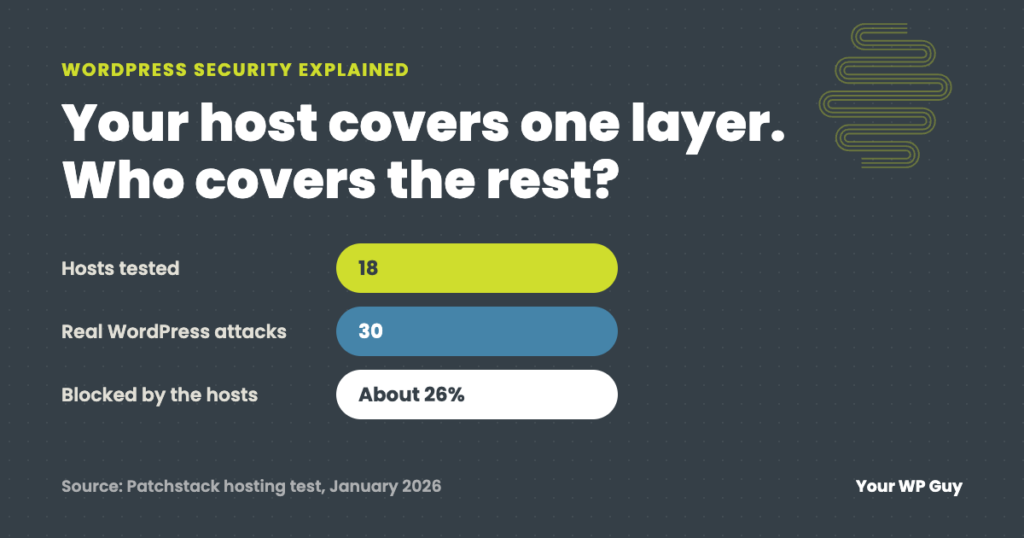
WordPress Security Explained: How the Layers Work Together (and Where Hosts Fall Short)
The short answer WordPress security is not one thing. It is layers: a firewall in front of the site, the server it runs on, WordPress itself, the plugins and theme, and the people who log in. Each layer catches what the others miss. Most hosts protect the server well but not WordPress: in an independent…
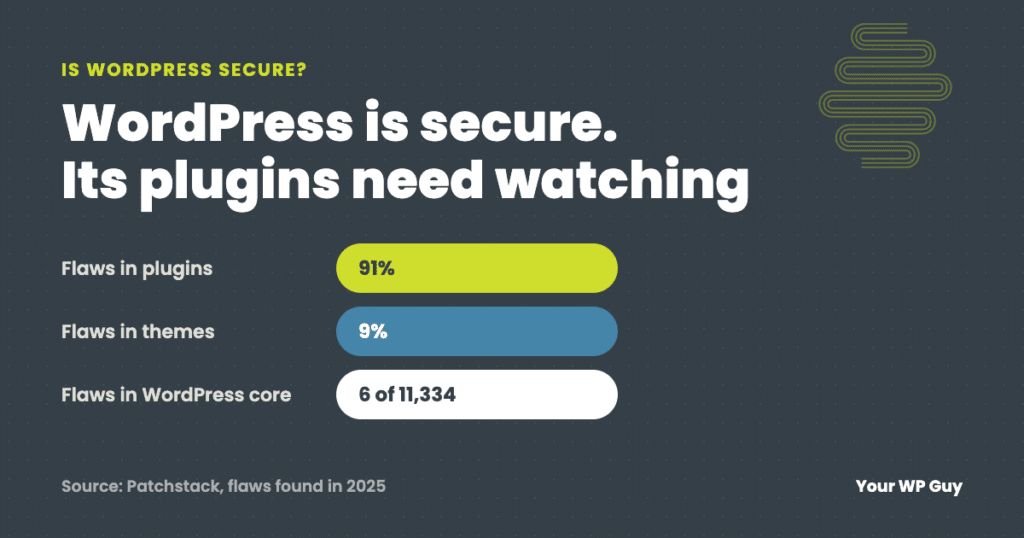
Is WordPress Secure? The Real Security Issues and How Sites Get Hacked
The short answer Yes, WordPress itself is secure: only 6 of the 11,334 WordPress security flaws found in 2025 were in WordPress core, all low priority. The real security issues are plugins (91%) and themes (9%), weak logins, and updates that wait too long, because attacks on a new flaw often start within hours, and…
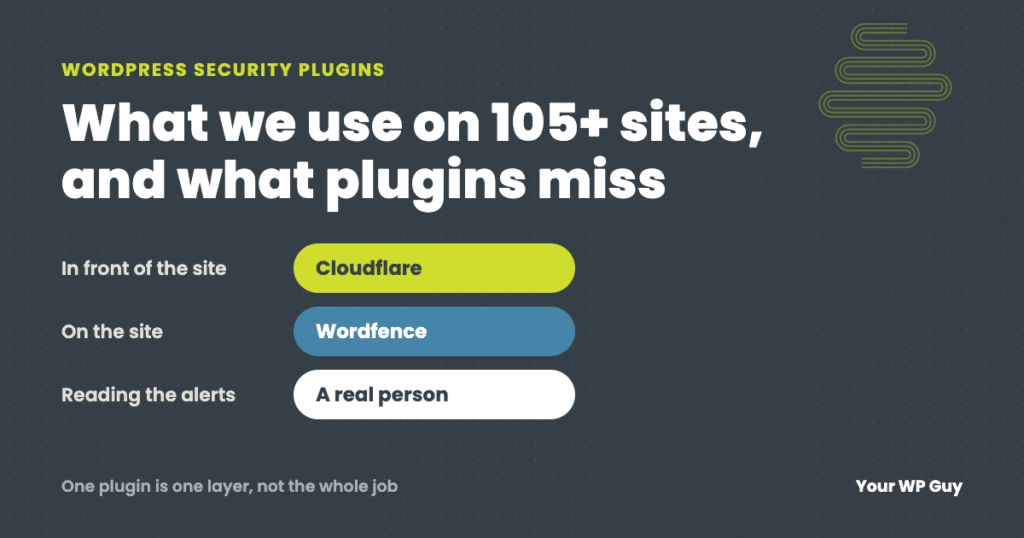
Best WordPress Security Plugins: What We Use on 105+ Sites
The short answer For most WordPress sites, the best security plugin is Wordfence, with Cloudflare in front of the site. Wordfence gives you a firewall, malware scanning and login protection in one plugin. Cloudflare stops bad traffic before it reaches your server. Run one all-in-one security plugin, not two. A plugin is only one layer,…
Case Study: The Invisible WordPress Outage Every Monitor Called “Up”
A WordPress site returned a healthy 200 status on every page for 33 hours while completely broken, undetected by uptime monitoring. Here is how we found and fixed an invisible outage in under three hours, and the critical vulnerability the update was patching.
Bot Traffic Attack Case Study: Stopped Before Any Downtime
The Short Version A site we manage took a massive traffic surge one morning: many times its normal volume, all inside a single hour. It was a bot traffic attack. Nothing was broken yet, but that kind of flood takes a server down fast once it tips over. Our monitoring knows what normal looks like…
WordPress Site Monitoring: What We Actually Watch
Most WordPress maintenance providers monitor 4 to 6 things, mostly unverified. Here is the full stack we run on every site we manage, and the real example that shows why it matters.
Card Testing Attack? How to Spot and Stop It on Your Store
TL;DR Card testing is a bot running stolen card numbers through your checkout to find out which ones still work. It is not trying to buy anything from you. The giveaway is a burst of declined orders with fake names, fake emails, and the same small charge amount hit over and over. Every declined attempt…
What a Real WordPress Site Attack Looks Like (And How We Stopped It)
Most articles about WordPress security talk in generalities: keep your plugins updated, use strong passwords, install a firewall. This post is different. This is a real WordPress site attack that hit one of our client sites on July 13, 2026, told with the actual numbers, the actual IP addresses, and the actual fixes we deployed…