wordpress security
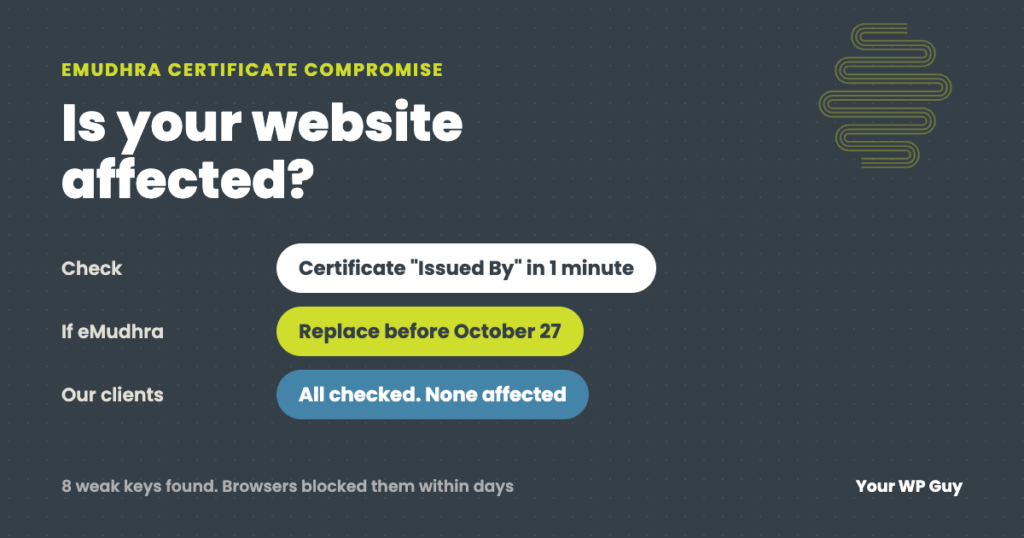
eMudhra Certificate Compromise: Is Your Website Affected?
The short answer In October 2026, eight intermediate certificates from the certificate authority eMudhra were found to have private keys so weak that anyone could recover them. In theory that let someone create a fake certificate for any website. Browsers blocked the certificates within days, and no misuse has been confirmed. Your website is only…
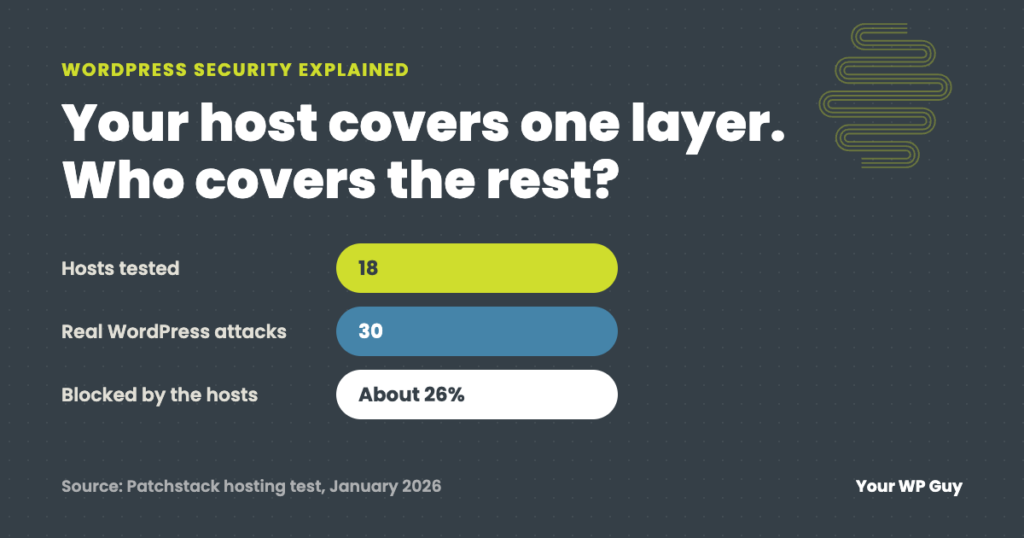
WordPress Security Explained: How the Layers Work Together (and Where Hosts Fall Short)
The short answer WordPress security is not one thing. It is layers: a firewall in front of the site, the server it runs on, WordPress itself, the plugins and theme, and the people who log in. Each layer catches what the others miss. Most hosts protect the server well but not WordPress: in an independent…
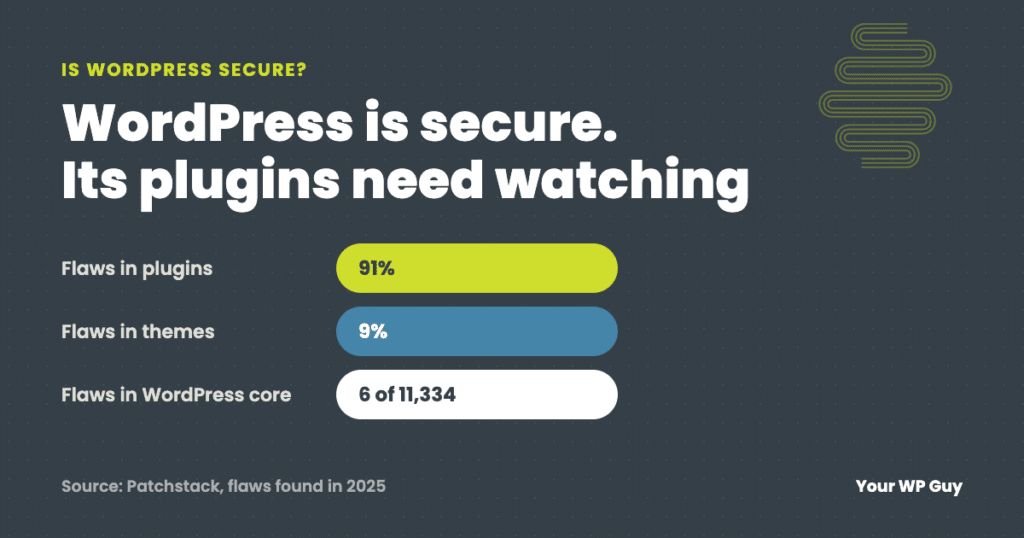
Is WordPress Secure? The Real Security Issues and How Sites Get Hacked
The short answer Yes, WordPress itself is secure: only 6 of the 11,334 WordPress security flaws found in 2025 were in WordPress core, all low priority. The real security issues are plugins (91%) and themes (9%), weak logins, and updates that wait too long, because attacks on a new flaw often start within hours, and…
Best WordPress Security Plugins: What We Use on 105+ Sites
The short answer For most WordPress sites, the best security plugin is Wordfence, with Cloudflare in front of the site. Wordfence gives you a firewall, malware scanning and login protection in one plugin. Cloudflare stops bad traffic before it reaches your server. Run one all-in-one security plugin, not two. A plugin is only one layer,…
Case Study: The Invisible WordPress Outage Every Monitor Called “Up”
A WordPress site returned a healthy 200 status on every page for 33 hours while completely broken, undetected by uptime monitoring. Here is how we found and fixed an invisible outage in under three hours, and the critical vulnerability the update was patching.

Yoast SEO – Advanced SEO with real-time guidance and built-in AI Vulnerability – Authenticated (Contributor+) Stored Cross-Site Scripting via ‘jsonText’ Block Attribute – CVE-2026-3427 | WordPress Plugin Vulnerability Report
Plugin Name: Yoast SEO – Advanced SEO with real-time guidance and built-in AI Key Information: Software Type: PluginSoftware Slug: wordpress-seoSoftware Status: ActiveSoftware Author: yoastSoftware Downloads: 930,902,675Active Installs: 10,000,000Last Updated: March 22, 2026Patched Versions: 27.2Affected Versions: <= 27.1.1 Vulnerability Details: Name: Yoast SEO <= 27.1.1Title: Authenticated (Contributor+) Stored Cross-Site Scripting via ‘jsonText’ Block AttributeType: CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:NCVE: CVE-2026-3427CVSS…
The Events Calendar Vulnerability – Missing Authorization to Authenticated (Subscriber+) Data Migration Control – CVE-2025-15043 | WordPress Plugin Vulnerability Report
Plugin Name: The Events Calendar Key Information Software Type: PluginSoftware Slug: the-events-calendarSoftware Status: ActiveSoftware Author: stellarwpSoftware Downloads: 78,686,265Active Installs: 700,000Last Updated: January 22, 2026Patched Versions: 6.15.13.1Affected Versions: ≤ 6.15.13 Vulnerability Details Name: The Events Calendar ≤ 6.15.13 – Missing Authorization to Authenticated Data Migration ControlTitle: Missing Authorization to Authenticated (Subscriber+) Data Migration ControlType: Missing Authorization…
Newsletter – Send awesome emails from WordPress Vulnerability – Cross-Site Request Forgery to Newsletter Unsubscription – CVE-2026-1051 | WordPress Plugin Vulnerability Report
Plugin Name: Newsletter – Send awesome emails from WordPress Key Information Software Type: PluginSoftware Slug: newsletterSoftware Status: ActiveSoftware Author: satolloSoftware Downloads: 32,725,200 Active Installs: 300,000 Last Updated: January 20, 2026 Patched Versions: 9.1.1 Affected Versions: ≤ 9.1.0 Vulnerability Details Name: Newsletter – Send awesome emails from WordPress ≤ 9.1.0 Title: Cross-Site Request Forgery to Newsletter UnsubscriptionType:…
Custom Fonts – Host Your Fonts Locally Vulnerability – Missing Authorization to Unauthenticated Font Deletion – CVE-2025-14351 | WordPress Plugin Vulnerability Report
Plugin Name: Custom Fonts – Host Your Fonts Locally Key Information Software Type: PluginSoftware Slug: custom-fontsSoftware Status: ActiveSoftware Author: brainstormforceSoftware Downloads: 6,158,177Active Installs: 300,000Last Updated: January 22, 2026Patched Versions: 2.1.17Affected Versions: ≤ 2.1.16 Vulnerability Details Name: Custom Fonts – Host Your Fonts Locally ≤ 2.1.16 Title: Missing Authorization to Unauthenticated Font DeletionType: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:NCVE: CVE-2025-14351CVSS Score: 5.3Publicly…
Essential Addons for Elementor – Popular Elementor Templates & Widgets Vulnerability – Missing Authorization to Unauthenticated Sensitive Information Exposure – CVE-2026-1004 | WordPress Plugin Vulnerability Report
Plugin Name: Essential Addons for Elementor – Popular Elementor Templates & Widgets Key Information Software Type: PluginSoftware Slug: essential-addons-for-elementor-liteSoftware Status: ActiveSoftware Author: wpdevteamSoftware Downloads: 117,159,772Active Installs: 2,000,000Last Updated: January 22, 2026Patched Versions: 6.5.6Affected Versions: ≤ 6.5.5 Vulnerability Details Name: Essential Addons for Elementor ≤ 6.5.5 – Missing Authorization to Unauthenticated Sensitive Information ExposureTitle: Missing Authorization…