How to Tell If Your WordPress Site Has Been Hacked (and What Is Not a Hack)
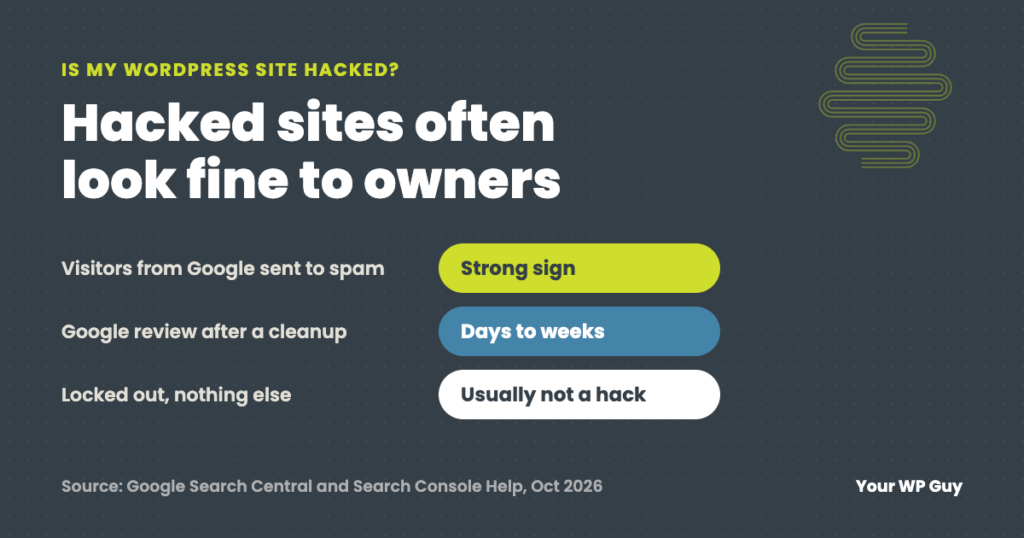
The strongest signs your WordPress site has been hacked: Google shows “This site may be hacked” or a red warning, visitors get sent to spam sites, there is an admin user you did not create, pages or files appear that nobody on your team made, or your host warns you about malware. A lockout, a slow site or spam comments on their own usually are not a hack. Already sure you were hacked?
Many hacked WordPress sites look fine to their owners. Your homepage loads, your dashboard works, and meanwhile visitors coming from Google land on a pharmacy store, or Google quietly finds thousands of spam pages under your domain. Hackers want the site to keep working, because a working site is worth more to them.
We look after WordPress sites for small businesses every day and clean up hacked ones, so this guide covers what we actually check: the signs, sorted by where you would notice them, how to check each one safely, and the red flags that turn out not to be a hack at all.
Why you may be the last to see it
Hacked sites often show different things to different people. Google’s own documentation says a hacked page can redirect visitors who click from Google search results but not someone who types the address in. Other hacks only fire on phones, or only for visitors who are not logged in. Spam pages can show the owner a blank page or a “not found” page while Google sees the spam.
So check the way a stranger would:
- Search your own domain. Type this into Google, with your domain in place of the example:
Look for pages you never made, titles in another language, or words like pharmacy, casino or replica brands.site:yourdomain.com - Click through from Google in a private window, logged out, on a phone using cell data instead of your office Wi-Fi.
- Use the URL Inspection tool in Google Search Console. It shows the page the way Google saw it, which can be different from what you see.
If you already suspect a page is infected, Google advises against opening it in your browser. Use the URL Inspection tool, or ask someone who can check it safely.
What Google shows when it thinks you are hacked
Google uses different warnings for different problems. The exact wording tells you which one you have:
| What you see | Where | What it means |
|---|---|---|
| “This site may be hacked” | Under your listing in Google search results | Google believes someone changed your pages or added spam pages, and visitors may be redirected to spam |
| “This site may harm your computer” | Under your listing in Google search results | Google believes the site may try to install malicious software on visitors’ computers |
| A red “Dangerous site” page | In Chrome, before your site loads | Google Safe Browsing flagged the site for malware, phishing or similar |
| An entry under Security Issues | Google Search Console | The official list: hacked content, malware or social engineering, with sample pages |
Google says its warnings depend on how someone browses, so you may not be able to see them yourself. The Security Issues report in Search Console is the place to confirm. Its list of sample pages is not necessarily complete, and once the site is clean you request a review. Google says reviews can take several days or weeks, so a fast cleanup matters.
One more Google sign: if Search Console emails you that someone you do not know was added as an owner of your site, Google calls that a strong possibility your site has been hacked. Hackers add themselves so they can control how their spam pages show up in search.
Signs inside WordPress
- An admin user you did not create. Go to Users and filter by Administrator. Check every account, including old ones that look official. In a breach we cleaned up, the unknown admin got in through a plugin flaw, with no login attempt anywhere.
- Posts, pages or links nobody on your team wrote. Check recent posts, pages and drafts, and look for links in old posts that point somewhere strange.
- Plugins you did not install, or a plugin that does not show in the list but has a folder on the server.
- Settings that changed by themselves, such as the site address or the admin email under Settings, then General.
If your host gives you WP-CLI, these commands list every administrator and compare WordPress’s own files and your plugins against the official copies:
wp user list --role=administrator
wp core verify-checksums
wp plugin verify-checksums --all
A failed checksum is worth a closer look, not proof of a hack. We have seen WordPress 7.x’s own new files reported as “should not exist” by these checks, and premium plugins that are not on WordPress.org cannot be checked this way.
Signs on the server, in your inbox and in your store
On the server and from your host
- PHP files in your uploads folder. The uploads folder holds images and documents, and it should not contain PHP files. From your WordPress folder, this lists any it finds:
find wp-content/uploads -name "*.php" - A warning or suspension from your host. Your host can see the whole server, including traffic you cannot. Take its malware warnings seriously, and ask exactly which files it flagged.
- Old folders next to WordPress. An old site, a test copy or a forgotten folder sitting beside WordPress can be hacked even when WordPress is clean, and many scanners only look at WordPress’s own folders.
- Warnings on your backups. A backup that finishes with warnings about unreadable or unusually large files is worth reading. That is how the hack in the story below was found.
In your inbox
WordPress emails you when certain things change. If you get one of these and did not make the change, treat it as a strong sign:
- “Admin Email Changed”, sent to the old admin address
- “Password Changed” or “Email Changed” for your account
- “New User Registration” for a user you do not know
The silence matters too. An account created by malicious code does not always trigger an email, so check the user list even if your inbox is quiet.
In your store
If customers report fraud on cards they used at your checkout, the checkout itself may have been tampered with, and that needs a cleanup right away. A burst of small failed orders is different: that is usually card testing, an attack on your checkout rather than a hacked site.
Red flags that usually are not a hack
Not every scare is a hack. These deserve a check, but they usually have another cause:
| What you notice | The usual cause | Where to start |
|---|---|---|
| You are locked out | A security plugin, your host or a firewall blocked the login. WordPress itself never locks you out | Login errors |
| The site is slow or down | A bot flood, a plugin or the server, not a break-in | What to check when the site is down, or what an attack looks like |
| A blank page or “critical error” | A plugin or theme crashed | Fix the critical error |
| Spam comments | Bots post to every open comment form | Turn on comment moderation or an anti-spam plugin |
| “Not secure” in the address bar | An SSL certificate or https setting | Check the certificate with your host |
| Your site is blocked on one network only | A network filter wrongly flagged it | A false phishing flag |
| Spam sites linking to yours | Links pointing at you, not a change on your server | Hidden spam links inside your own pages are the real sign |
Security tools raise false alarms too. In cases we have checked, a plugin’s “critical” findings were WordPress’s own new files, “unknown files” were empty leftovers from a cleanup years earlier, and a host’s “injection detected” email was about a clean file in a forgotten test copy of the site, not the live site. Confirm before you delete anything.
A real example: the hack nobody saw for almost six years
On the first day of a new care plan for a membership association, the site’s first off-site backup finished with two warnings: a file it could not read, and an unusually large file anyone could download. The site looked and loaded normally, and its security scanner had reported nothing.
Following those warnings led to folders from the association’s old website, built before WordPress, that were never removed. Inside were hidden backdoors, upload scripts, pharmacy spam pages and three copies of a fake Dropbox login page used to phish other people in the association’s name. There had been two separate break-ins, one in 2014 and one in December 2020, and the newer one had gone unnoticed for almost six years. The scanner only checked WordPress’s own folders. We contained everything the same day, moving the files out of reach instead of deleting them, changed the access passwords, and turned on daily monitoring, with no downtime.
Think you are hacked? Do this, not that
- Don’t start deleting. A backdoor can recreate a deleted admin on the next page load, and deleted files are evidence of how they got in.
- Take a backup first, labeled as infected, so nothing is lost and the cleanup has a starting point.
- Write down what you saw: the warning text, the pages, the users, and when you noticed.
- Get it cleaned properly. A cleanup has to remove every backdoor and close the hole, or the site gets reinfected. Our Emergency Clean Up is a $249 flat rate, and it is free for sites on our care plans.
Not sure what you are looking at?
Send us what you found and we will tell you whether it is a hack, and clean it up if it is.
- Tell us what you seeThe warning, the strange page or the user you don’t recognize.
- We check it safelyWe confirm what is real, find every backdoor and close the way in.
- You get back to your businessWith a clean site and a plain-English note on what happened.
Want to know how exposed your site is? Our free Uh Oh Score checks your site and shows what to fix first, with no sales call required.
Get my Uh Oh ScoreQuestions people ask
How can I tell if my WordPress site has been hacked?
The strongest signs are a Google warning such as “This site may be hacked”, visitors being sent to spam sites, an admin user you did not create, pages or files nobody on your team made, and a malware warning from your host. Search site:yourdomain.com in Google and check the Security Issues report in Search Console.
What does “This site may be hacked” mean in Google?
Google believes someone changed pages on your site or added spam pages, and that visitors may be redirected to spam or malware. Check the Security Issues report in Search Console for sample pages, clean the site and close the way in, then request a review. Google says reviews can take several days or weeks.
Why does my site only redirect to spam on my phone or from Google?
Many hacks only redirect certain visitors, such as people who click from Google search results, use a phone or are not logged in, so the owner never sees it. That pattern is a strong sign of a hack, not a glitch.
Is being locked out a sign my site was hacked?
Usually not on its own. Most lockouts come from a security plugin, your host or a firewall. It points to a hack when it comes with other signs, like a “Password Changed” or “Admin Email Changed” email you did not trigger or an admin you do not know.
Can a malware scan tell me my site is clean?
A clean scan is good news, not proof. Scanners can miss new backdoors, and many only check WordPress’s own folders, not old sites or test copies sitting next to it. Check users, recent changes and your server folders too.
What is website defacement?
Defacement is when someone changes what your site shows, such as replacing the homepage with their own message. It is the visible part of a hack, so the way in and any hidden backdoors still need to be found and removed.
My security plugin or host says I am infected. Is it real?
Often, but not always. We have seen WordPress’s own new files, empty leftovers from an old cleanup and clean files in a forgotten test copy all reported as infections. Ask exactly which files were flagged, and confirm before deleting anything.
Sources
- Google Search Help, “This site may be hacked” and “This site may harm your computer” (checked October 2026).
- Google Search Console Help, Security Issues report.
- Google Search Central, Spam policies: hacked content, and web.dev, Fix the Japanese keyword hack.
- Google Chrome Help, Manage warnings about unsafe sites.
- WordPress 7.1.3 source code, user.php and pluggable.php (account change emails).
Keep your website working as hard as you do
We update, back up, monitor and protect your WordPress site every day, and if a site on our plans is ever hacked, the cleanup is included.
Jonathan Wofford is the founder of Your WP Guy, a WordPress care and maintenance service supporting 105+ active client sites. He and his team keep WordPress sites fast, secure, and running, so business owners can stay focused on their business instead of their website.