Photo Gallery by 10Web Vulnerability – Directory Traversal to Arbitrary File Rename – CVE-2024-0221 | WordPress Plugin Vulnerability Report

Plugin Name: Photo Gallery by 10Web Key Information: Software Type: Plugin Software Slug: photo-gallery Software Status: Active Software Author: 10web Software Downloads: 17,512,296 Active Installs: 200,000 Last Updated: January 19, 2024 Patched Versions: 1.8.20 Affected Versions: <= 1.8.19 Vulnerability Details: Name: Photo Gallery by 10Web – Mobile-Friendly Image Gallery <= 1.8.19 – Directory Traversal to Arbitrary File Rename Type: Improper Limitation of a Pathname to a…
Read MoreThe Events Calendar Vulnerability – Unauthenticated Sensitive Information Exposure – CVE-2023-6557 | WordPress Plugin Vulnerability Report
Plugin Name: The Events Calendar Key Information: Software Type: Plugin Software Slug: the-events-calendar Software Status: Active Software Author: theeventscalendar Software Downloads: 53,054,073 Active Installs: 700,000 Last Updated: January 12, 2024 Patched Versions: 6.2.9 Affected Versions: <= 6.2.8.2 Vulnerability Details: Name: The Events Calendar <= 6.2.8.2 Title: Unauthenticated Sensitive Information Exposure Type: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N CVE: CVE-2023-6557 CVSS…
Read MoreHappy Addons for Elementor Vulnerability – Reflected Cross-Site Scripting – CVE-2023-6632 | WordPress Plugin Vulnerability Report
Plugin Name: Happy Addons for Elementor Key Information: Software Type: Plugin Software Slug: happy-elementor-addons Software Status: Active Software Author: thehappymonster Software Downloads: 5,728,647 Active Installs: 400,000 Last Updated: January 5, 2024 Patched Versions: 3.10.0 Affected Versions: <= 3.9.1.1 Vulnerability Details: Name: Happy Addons for Elementor <= 3.9.1.1 – Reflected Cross-Site Scripting Title: Reflected Cross-Site Scripting Type: Improper Neutralization of Input During Web Page Generation (‘Cross-site Scripting’) CVE: CVE-2023-6632…
Read MoreDepicter Slider Vulnerability – Cross-Site Request Forgery via save – CVE-2023-6493 | WordPress Plugin Vulnerability Report
Plugin Name: Depicter Slider Key Information: Software Type: Plugin Software Slug: depicter Software Status: Active Software Author: averta Software Downloads: 727,890 Active Installs: 80,000 Last Updated: January 4, 2024 Patched Versions: 2.0.7 Affected Versions: <= 2.0.6 Vulnerability Details: Name: Depicter Slider – Responsive Image Slider, Video Slider & Post Slider <= 2.0.6 – Cross-Site Request Forgery via save Title: Cross-Site Request Forgery via save Type: Cross-Site Request…
Read MoreWordPress Plugin Vulnerability Report – Backup Migration – Unauthenticated Remote Code Execution – CVE-2023-6553
Plugin Name: Backup Migration Key Information: Software Type: Plugin Software Slug: backup-backup Software Status: Active Software Author: migrate Software Downloads: 1,095,099 Active Installs: 90,000 Last Updated: December 11, 2023 Patched Versions: 1.3.8 Affected Versions: <= 1.3.7 Vulnerability Details: Name: Backup Migration <= 1.3.7 – Unauthenticated Remote Code Execution Type: Improper Control of Generation of Code (‘Code Injection’) CVE: CVE-2023-6553 CVSS Score: 9.8 (Critical) Publicly Published: December 11, 2023 Researcher: Nex…
Read MoreWordPress Plugin Vulnerability Report – SpeedyCache – Missing Authorization via speedycache_create_test_cache

Plugin Name: SpeedyCache Key Information: Software Type: Plugin Software Slug: speedycache Software Status: Active Software Author: softaculous Software Downloads: 746,740 Active Installs: 100,000 Last Updated: December 1, 2023 Patched Versions: 1.1.3 Affected Versions: <= 1.1.2 Vulnerability Details: Name: SpeedyCache <= 1.1.2 – Missing Authorization via speedycache_create_test_cache Title: Missing Authorization via speedycache_create_test_cache Type: Missing Authorization CVSS Score: 4.3 (Medium) Publicly Published: December 1, 2023 Description: The SpeedyCache – Cache, Optimization, Performance…
Read MoreAvoiding DIY Pitfalls: Why Professional Support Matters

Managing a business is already a challenge. Now throw in managing a website without expertise. Juggling too much at once is sure to lead to some dropped balls. And when your head is in a thousand places at once, even minor issues can quickly escalate into major headaches and lost revenue. Consider This A small…
Read MoreLocked Out of WordPress? What Your Login Error Means and How to Get Back In
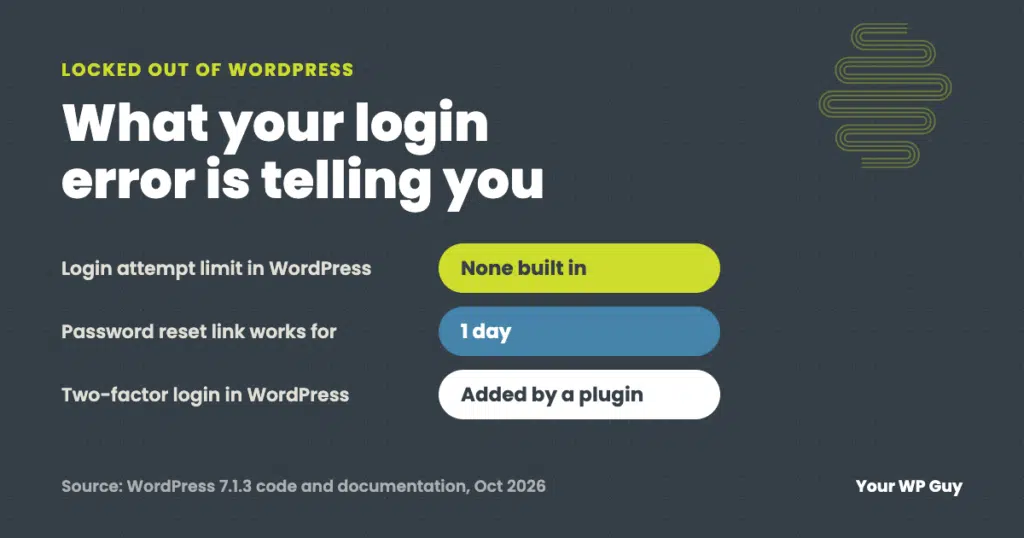
The short answer Most WordPress login problems come down to four things: a wrong username or password, a password reset email that never arrives, a lockout (from a security plugin, your host or a firewall), or a login page that keeps sending you back. The exact message on the login screen tells you which one…
Read More“Is It Just Me?”: Tools to Check the Availability of Your Website Worldwide

Having a consistently available website is crucial for any business competing digitally today. But maintaining website availability can be a major pain point, especially for small businesses with limited resources. When your site suffers downtime or simply becomes inaccessible for customers, the costs are very real—from immediate sales losses during outages to long-term brand reputation…
Read MoreHow to Tell If Your WordPress Site Has Been Hacked (and What Is Not a Hack)
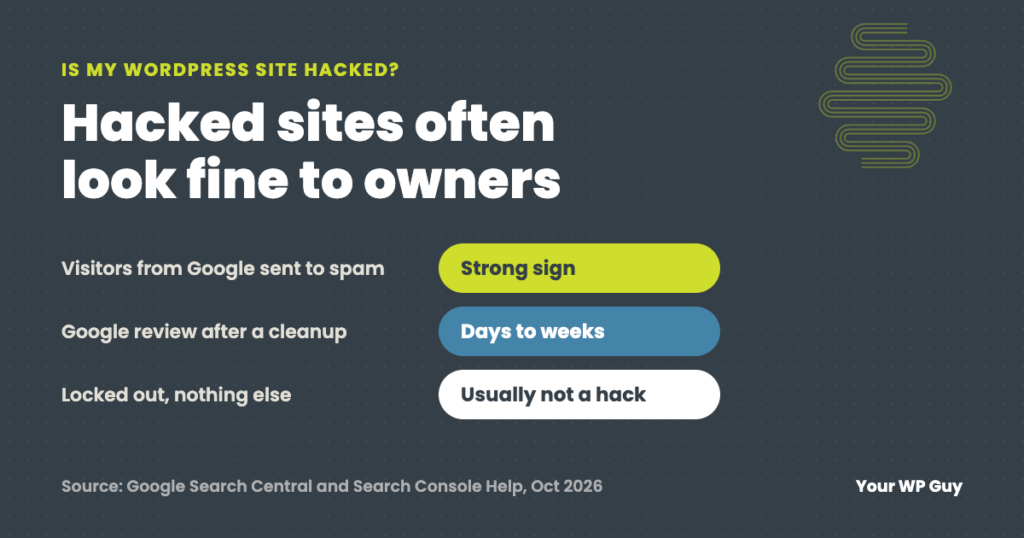
The short answer The strongest signs your WordPress site has been hacked: Google shows “This site may be hacked” or a red warning, visitors get sent to spam sites, there is an admin user you did not create, pages or files appear that nobody on your team made, or your host warns you about malware.…
Read More