The High Cost of Waiting: Real-world Impacts of Slow Support Responses

Your website crashes during a sale. Pages load at a crawl. Online forms stop working. You reach out for support, only to wait helplessly as the precious minutes tick by without resolution. The lackadaisical response from your website management team obstructs progress and drains productivity across your business. As a small business owner, you feel…
Read MoreWordPress Plugin Vulnerability Report – Comments – wpDiscuz – Unauthenticated SQL Injection

Plugin Name: Comments – wpDiscuz Key Information: Software Type: Plugin Software Slug: wpdiscuz Software Status: Active Software Author: advancedcoding Software Downloads: 2,865,421 Active Installs: 80,000 Last Updated: September 18, 2023 Patched Versions: 7.6.6 Affected Versions: <=7.6.5 Vulnerability Details: Name: wpDiscuz <= 7.6.5 – Unauthenticated SQL Injection Type: Improper Neutralization of Special Elements used in an…
Read MoreWordPress Plugin Vulnerability Report – Migration, Backup, Staging – WPvivid – Missing Authorization & Stored Cross-Site Scripting
Plugin Name: Migration, Backup, Staging – WPvivid Key Information: Software Type: Plugin Software Slug: wpvivid-backuprestore Software Status: Active Software Author: wpvividplugins Software Downloads: 5,141,419 Active Installs: 300,000 Last Updated: September 12, 2023 Patched Versions: 0.9.91 Affected Versions: <=0.9.90 First Vulnerability: Vulnerability Details: Name: WPvivid Backup Plugin <= 0.9.90 – Missing Authorization via ‘start_staging’ and ‘get_staging_progress’…
Read MoreWordPress Plugin Vulnerability Report: Slimstat Analytics – Authenticated (Contributor+) Blind SQL Injection via Shortcode – CVE-2023-4598
Key Information: Software Type: Plugin Software Slug: wp-slimstat Software Status: Active Software Author: mostafas1990 Software Downloads: 5,922,898 Active Installs: 100,000 Last Updated: September 11, 2023 Patched Versions: 5.0.10 Affected Versions: <=5.0.9 Vulnerability Details: Name: Slimstat Analytics <= 5.0.9 – Authenticated (Contributor+) Blind SQL Injection via Shortcode Type: Improper Neutralization of Special Elements used in an…
Read MoreWordPress Plugin Vulnerability Report: EWWW Image Optimizer – Sensitive Information Exposure
Plugin Name: EWWW Image Optimizer Key Information: Software Type: Plugin Software Slug: ewww-image-optimizer Software Status: Active Software Author: nosilver4u Software Downloads: 33,159,954 Active Installs: 1,000,000 Last Updated: September 7, 2023 Patched Versions: 7.2.1 Affected Versions: <7.2.1 Vulnerability Details: Name: EWWW Image Optimizer <= 7.2.0 – Sensitive Information Exposure Type: Information Exposure CVSS Score: 5.3 (medium)…
Read MoreWordPress Plugin Vulnerability Report: EmbedPress – Cross-Site Request Forgery
Plugin Name: EmbedPress Key Information: Software Type: Plugin Software Slug: embedpress Software Status: Active Software Author: wpdevteam Software Downloads: 1,709,151 Active Installs: 80,000 Last Updated: September 8, 2023 Patched Versions: 3.8.4 Affected Versions: <3.8.4 Vulnerability Details: Name: EmbedPress <= 3.8.3 – Cross-Site Request Forgery Type: Cross-Site Request Forgery (CSRF) CVSS Score: 4.3 (Medium) Publicly Published:…
Read MoreWordPress Plugin Vulnerability Report: User Feedback – Unauthenticated Stored Cross-Site Scripting – CVE-2023-39308
Plugin Name: User Feedback Key Information: Software Type: Plugin Software Slug: userfeedback-lite Software Status: Active Software Author: smub Software Downloads: 348,588 Active Installs: 100,000 Last Updated: September 7, 2023 Patched Versions: 1.0.8 Affected Versions: <=1.0.7 Vulnerability Details: Name: User Feedback <= 1.0.7 – Unauthenticated Stored Cross-Site Scripting Type: Improper Neutralization of Input During Web Page…
Read MoreBroken Website Emergency: First Steps to Diagnose and Fix

It’s every business owner’s nightmare – you wake up one morning to find your website is down. Or even worse, it’s up but full of glaring errors. Customers are complaining they can’t access your site or complete purchases. Your daily traffic has plummeted. Panic sets in. What caused this? Who can fix it? How quickly…
Read MoreAbandoned WordPress Plugins: How to Spot Them and What to Do
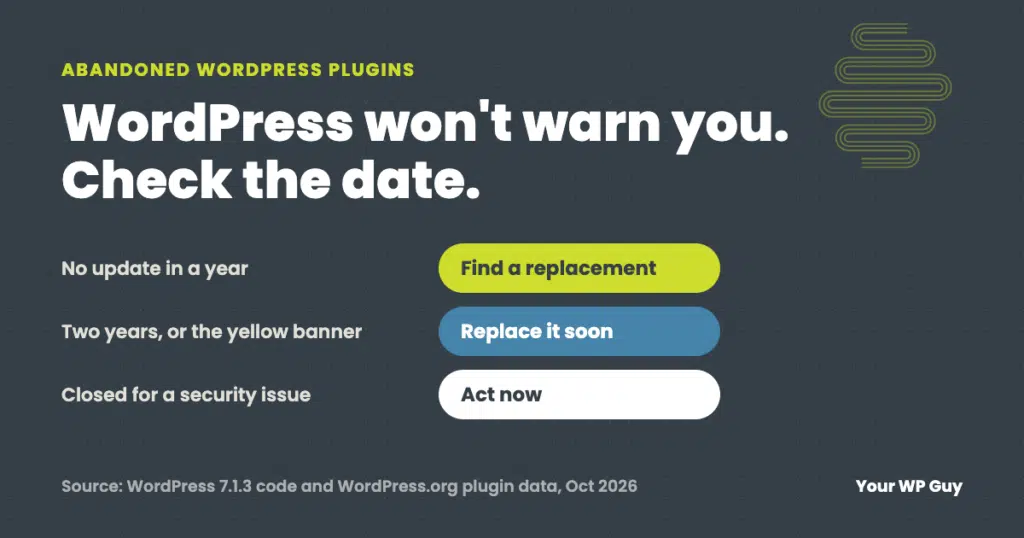
The short answer An abandoned WordPress plugin is one its developer no longer updates. It may keep working for years, but any security hole found in it will never be fixed, and it can break the next time WordPress or PHP changes. WordPress does not warn you, so check each plugin’s “Last updated” date. No…
Read MoreWhat Are the Risks of Not Performing WordPress Maintenance?

Running a business? It’s a bit like a high-stakes game of whack-a-mole, isn’t it? Always something popping up that needs your attention. And if you’re operating a WordPress site, you’ve got one more mole to keep an eye on. But here’s the thing: WordPress, while fantastic, is the most popular CMS on the Internet, and…
Read More